Will smart glasses make it too risky to speak up in class? — from timeshighereducation.com by Georgia Luckhurst & Kieran Phelan
AI-powered glasses may boost learning but they also pose obvious threats to privacy, academic integrity and the sanctity of the seminar room as a safe space to explore ideas. Are universities doing enough to head off the risks, asks Georgia Luckhurst – while Kieran Phelan suggests they are not

Smart glasses can superimpose information on to a viewer’s field of vision, and they can access apps and communicate with your phone. Some are hands-free while some require touch, and some also respond to voice automation. Most controversially, they can take pictures and record footage, potentially without anyone else knowing that it is happening. And they are becoming ever more common.

But, for academia, the biggest issue associated with smart glasses may be a decline in intellectual risk-taking and freedom of expression, Murray said.


How useful are smart glasses in improving accessibility in higher education? — from timeshighereducation.com by Helen Nicholson-Benn
Smart glasses have the potential to support learning for disabled students, but this technology also comes with significant privacy concerns. Helen Nicholson-Benn looks at how to balance functional benefits with data security and safeguarding

Consider how different models of smart glasses might be used to improve accessibility in higher education. A deaf student might use XRai’s ar2 captioning glasses during a lecture to view live captions in their eyeline, allowing them to follow the content without looking down at a separate screen. A visually impaired student might use Envision’s Ally Solos glasses to generate a description of images on printed material or read text during a class. The glasses provide a hands-free option rather than scanning the materials with their smartphone.

These examples are hypothetical, and smart glasses are far from an everyday teaching tool, but that may be about to change. Smart glasses available today are far more capable than their predecessors, particularly boosted by developments in artificial intelligence (AI) technology.


Which brings up the topic of how to handle these technologies in the classroom:

Are device-free classrooms the way forward? — from timeshighereducation.com by Georgia Luckhurst
US universities embrace laptop and phone bans, but professor suggests policies may be more about political positioning than pedagogy

Growing numbers of US universities are making some of their courses “device free”, drawing mixed enthusiasm from edtech experts.

In the latest move the University of Chicago is introducing a no-laptops and no-phones policy on three of its 15 required undergraduate modules, aiming to “reduce distractions and encourage face-to-face discussions”. Exceptions remain, including for students with disabilities.
…
Device-free policies appear in other countries, experts suggested, despite the trend picking up pace in the US.

 

Risks and Rewards of IoT in Higher Education — from edtechmagazine.com by Akeya Dickson
Shadow IT is flooding college and university networks as students move back to campus. Here’s how higher ed IT leaders can secure their networks without impacting the student experience.

Connected minifridges, smart speakers and internet-based gaming consoles are among the devices students are bringing to college that IT departments may not have accounted for — or even know are connected to the campus network. These devices may run on default passwords and have little to no security configuration, making them an attractive and vulnerable entry point for a cyberattack.

For higher ed IT, the stakes couldn’t be higher. According to the Zscaler ThreatLabz 2025 Mobile, IoT and OT Threat Report, the education sector saw an 861% rise in malware attacks from Internet of Things devices between 2024 and 2025.


Dario Amodei’s article here:
We Must Pace the Frontier — from darioamodei.com

But like many technologies before it, AI brings risks, and because it is such a powerful technology, these risks are serious. I’ve written a lot about them too. They include the risk of losing control of AI systems, misuse of AI for cyberattacks and bioterrorism, and serious economic disruption. A race to the bottom, spurred by commercial incentives, can make these risks more acute.

Along with my co-founders and employees, I have grappled with this duality of risk and benefit since the beginning of Anthropic.


Also relevant/see:


[GIFTED ARTICLE]
Anthropic CEO calls for the AI industry to slow down — from washingtonpost.com by Ted Hesson, Ian Duncan, and Gerrit De Vynck
Anthropic CEO Dario Amodei said he was worried about the ability to control self-improving AI models.

Three of the nation’s leading artificial intelligence executives endorsed slowing down the blistering pace of technological advancement, revealing the growing unease with its potential dangers at the industry’s very highest levels.

The call was first made in an essay Anthropic chief executive Dario Amodei posted online Saturday. The idea has gained ground in recent weeks as AI companies have struggled in some cases to keep their creations under control, even as they usher in an age in which AI systems themselves can build the more powerful next generation of the technology.


[GIFTED ARTICLE]
For years, they warned AI could kill all humans. Now people are listening. — from washingtonpost.com by Nitasha Tiku
A doomsaying community once on the periphery of the tech industry has gained influence, as AI “agents” perform amazing and alarming feats.

But when Hubinger issued a similar warning this week in a post on X, his message was viewed tens of millions of times, prompting state and federal lawmakers to echo his concern. Now he spoke as a team lead at Anthropic, developer of the chatbot Claude and a company set to go public at a valuation of over $1 trillion.

“AI could kill all humans … I personally think it is >10% within the next decade,” Hubinger wrote, in response to the resignation of his colleague Jacob Coxon, who accused Anthropic of racing ahead despite the dangers.
.


OpenAI’s chief scientist says no lab should keep scaling at maximum speed — from thenextweb.com by Ana Maria Constantin
OpenAI put out two posts on Sunday. Its research organisation now uses 3.1 agent-workdays for every human one, and its chief scientist says no lab has solved alignment well enough to keep scaling at full speed. The case for an OpenAI slowdown arrived with the numbers against it.

Chief scientist Jakub Pachocki wrote the second post, an essay called An Alien Mind. It closes on a line that reads oddly from the man who runs research at the company shipping fastest.

“Currently I believe that no lab has solved alignment and monitoring to a sufficient degree to continue responsibly scaling at maximum speed for much longer,” he wrote.

…
He is not gentle about the stakes either. “This is a time that calls for extreme caution. I am concerned no one is prepared for the consequences of a continued rapid rise in machine intelligence,” Pachocki wrote.


Employees from the world’s biggest AI companies want the US to be ready to slow AI development — from cnn.com by Hadas Gold

Top staffers from the biggest AI and technology companies urged the US government to slow the pace of artificial intelligence development so that safety and security measures can catch up in an open letter.

The US government should support an international effort to develop tools that can “deliberately pace the frontier of automated AI development,” according to the letter.

More than 1,000 employees from frontier AI companies signed the letter, including the chief scientist of OpenAI, one of the ChatGPT developer’s original cofounders, some of Anthropic’s cofoundersand vice presidents at Meta, Google and others.

The letter comes on the heels of major advancements and burgeoning threats from rapidly developing AI systems. OpenAI disclosed last week that two of its test models escaped a lab environment, bypassed its systems to gain access to the open internet and hacked a different company’s internal system.


Cybersecurity Researchers Identify First Fully Autonomous AI-Driven Ransomware Attack — from campustechnology.com by John K. Waters

Key Takeaways

  • Sysdig documented an AI agent independently chaining reconnaissance, credential theft, lateral movement, persistence, and destructive database encryption across more than 600 payloads, entering through an already-patched vulnerability rather than exploiting any novel AI capability.
  • The agent recovered from a failed step in just 31 seconds without human intervention, diagnosing and correcting a technical error on its own, a level of autonomous troubleshooting that researchers say marks a shift beyond earlier AI-assisted attacks.
  • Cybersecurity firm HiddenLayer reports that autonomous AI agents now account for roughly one in eight reported AI-related security breaches, suggesting JADEPUFFER reflects a broader industry trend rather than an isolated incident.
 

Researchers hid a prompt injection inside a PNG, and AI fell for it — from digitaltrends.com by Shimul Sood

A team of security researchers (professor Sudipta Chattopadhyay and researcher Murali Ediga) has demonstrated an unusual attack that doesn’t target the AI model directly. Instead, it targets what the AI doesn’t pay enough attention to during code reviews. Rather than hiding malicious instructions in lines of code, the researchers tucked them inside an image file. Since many AI review tools treat images as decorative assets rather than as something worth inspecting, the pull request can appear perfectly harmless and sail through the review.

They argue that AI review tools need to become “multimodal” in the truest sense — treating images, documentation, configuration files, and other non-code assets with the same level of scrutiny as source code. If an AI can read a picture, it also needs to understand that the picture could be trying to manipulate it. For developers, this is another reminder that AI coding tools still need supervision. They can dramatically speed up software development, but they also open entirely new attack surfaces that didn’t exist before. The next security risk might not be hidden in thousands of lines of code — it could be sitting inside an image that nobody thought was worth opening.


AI has already fallen into the wrong hands and they’re using it to make bombs — from digitaltrends.com by Shimul Sood

Artificial intelligence has quickly become the go-to tool for everything from writing emails and summarizing meetings to helping students study or developers debug code. But the same technology that saves people time can also be misused, and a new report suggests that terrorist organizations are finding ways to do exactly that.

According to a research paper shared with The New York Times ahead of its publication, researchers found evidence that members of Boko Haram have been using popular AI chatbots to support both day-to-day activities and combat-related tasks. Interviews with 27 former members conducted in Nigeria over the past two years suggest that tools such as ChatGPT, Gemini, Claude, Grok, Meta AI, and DeepSeek were used to gather technical information, troubleshoot weapons, and even assist with planning attacks.

This wasn’t just a few bad actors messing around
What makes the findings especially concerning is that this wasn’t described as the work of a few individuals experimenting with AI. The report claims the group’s use of AI had become organized, with dedicated teams, internal training, and knowledge shared between members. Researchers also say some users managed to bypass built-in safety protections designed to prevent AI from responding to requests related to violence.


A Comprehensive Report on Teens, Tweens, and AI — from commonsensemedia.org

To find out what that actually looks like day-to-day, we surveyed more than a thousand 9- to 17-year-olds across the country. We asked them how they use AI, how often, and for what.

The Common Sense Media Census: AI Use by Tweens and Teens (2026) is the first in a series we’ll repeat every year to learn how this generation’s relationship with AI evolves over time.

A few things stood out:

  • Kids are using AI for many things. It’s not just a homework helper anymore. For some kids, AI has become a confidant, even though our research is clear that AI companionship is not safe for anyone under 18.
  • Guardrails are thin to nonexistent. Schools are talking about rules more than safety. Three-quarters of kids say their school has discussed what they can and cannot use AI for, but just over half have been taught how to use AI safely.
  • Just like we saw with smartphones and social media, the conversation is once again lagging behind the technology. Nearly half of kids have never had a conversation with their parents about AI safety.
 

Job Scams Are Everywhere. Here’s How to Spot Them Before It’s Too Late. — from builtin.com by Alex Chepovoi
As people face increasing economic pressure, scammers are using fake job ads to harvest your data. Our expert explains the warning signs.

Summary: Scammers are flooding hiring platforms like LinkedIn with AI-generated fake remote jobs to steal data. Nearly 80 percent of these scams target low-skill roles, using inflated pay and vague requirements as bait. Platforms should adopt AI-driven detection to protect vulnerable job seekers.

Market desperation has become a growth engine for fraud. People invest their hope, time and personal data into an opportunity that doesn’t exist and could use their information for financial gains, identity theft or espionage. 

Until hiring platforms take greater responsibility for vetting the roles they host, the burden of staying safe falls on job seekers. Once you understand the motives and patterns scammers rely on, however, spotting them becomes much easier.

But a combination of vague descriptions, inflated pay, minimal requirements and subtle urgency is exactly what makes the system so effective.


A New Era of Security: Frontier AI Defense — from paloaltonetworks.com by Sam Rubin

For the last several months, we have had early, unbounded access to the latest frontier AI models. What we’ve seen from that vantage point has made it clear that the window for organizations to get ahead of what’s coming is shorter than most leaders realize.

We have moved past the era of incremental AI improvements into a threat landscape shift. Our testing has revealed a step-change in capability that demonstrates an intuitive understanding of software vulnerabilities. This is more than faster code generation, it is a shift from AI as an assistant to AI as an autonomous agent capable of discovering and chaining flaws at a scale that most defenders aren’t prepared for.

These capabilities will not stay confined to controlled environments for long. When Mythos first launched, we predicted a six-month window before attackers gained access. We now believe that timeline has accelerated significantly.


Report: No Foolproof Method Exists for Detecting AI-Generated Media — from campustechnology.com by Chris Paoli

Key Takeaways

  • Microsoft Research warns no foolproof method exists for detecting AI-generated media reliably.
  • C2PA provenance, watermarking, and fingerprinting each face security and reversal attack risks.
  • Combined high-confidence authentication and public education are crucial for AI media integrity.


AI working competency is now a graduation requirement at Purdue [Pacton] + other items re: AI in our learning ecosystems


AI Has Landed in Education: Now What? — from learningfuturesdigest.substack.com by Dr. Philippa Hardman

Here’s what’s shaped the AI-education landscape in the last month:

  • The AI Speed Trap is [still] here: AI adoption in L&D is basically won (87%)—but it’s being used to ship faster, not learn better (84% prioritising speed), scaling “more of the same” at pace.
  • AI tutors risk a “pedagogy of passivity”: emerging evidence suggests tutoring bots can reduce cognitive friction and pull learners down the ICAP spectrum—away from interactive/constructive learning toward efficient consumption.
  • Singapore + India are building what the West lacks: they’re treating AI as national learning infrastructure—for resilience (Singapore) and access + language inclusion (India)—while Western systems remain fragmented and reactive.
  • Agentic AI is the next pivot: early signs show a shift from AI as a content engine to AI as a learning partner—with UConn using agents to remove barriers so learners can participate more fully in shared learning.
  • Moodle’s AI stance sends two big signals: the traditional learning ecosystem in fragmenting, and the concept of “user sovereignty” over by AI is emerging.

Four strategies for implementing custom AIs that help students learn, not outsource — from educational-innovation.sydney.edu.au by Kria Coleman, Matthew Clemson, Laura Crocco and Samantha Clarke; via Derek Bruff

For Cogniti to be taken seriously, it needs to be woven into the structure of your unit and its delivery, both in class and on Canvas, rather than left on the side. This article shares practical strategies for implementing Cogniti in your teaching so that students:

  • understand the context and purpose of the agent,
  • know how to interact with it effectively,
  • perceive its value as a learning tool over any other available AI chatbots, and
  • engage in reflection and feedback.

In this post, we discuss how to introduce and integrate Cogniti agents into the learning environment so students understand their context, interact effectively, and see their value as customised learning companions.

In this post, we share four strategies to help introduce and integrate Cogniti in your teaching so that students understand their context, interact effectively, and see their value as customised learning companions.


Collection: Teaching with Custom AI Chatbots — from teaching.virginia.edu; via Derek Bruff
The default behaviors of popular AI chatbots don’t always align with our teaching goals. This collection explores approaches to designing AI chatbots for particular pedagogical purposes.

Example/excerpt:


Disrupting the first reported AI-orchestrated cyber espionage campaign — from Anthropic

Executive summary
We have developed sophisticated safety and security measures to prevent the misuse of our AI models. While these measures are generally effective, cybercriminals and other malicious actors continually attempt to find ways around them. This report details a recent threat campaign we identified and disrupted, along with the steps we’ve taken to detect and counter this type of abuse. This represents the work of Threat Intelligence: a dedicated team at Anthropic that investigates real world cases of misuse and works within our Safeguards organization to improve our defenses against such cases.

In mid-September 2025, we detected a highly sophisticated cyber espionage operation conducted by a Chinese state-sponsored group we’ve designated GTG-1002 that represents a fundamental shift in how advanced threat actors use AI. Our investigation revealed a well-resourced, professionally coordinated operation involving multiple simultaneous targeted intrusions. The operation targeted roughly 30 entities and our investigation validated a handful of successful intrusions.

This campaign demonstrated unprecedented integration and autonomy of AI throughout the attack lifecycle, with the threat actor manipulating Claude Code to support reconnaissance, vulnerability discovery, exploitation, lateral movement, credential harvesting, data analysis, and exfiltration operations largely autonomously. The human operator tasked instances of Claude Code to operate in groups as autonomous penetration testing orchestrators and agents, with the threat actor able to leverage AI to execute 80-90% of tactical operations independently at physically impossible request rates.

From DSC:
The above item was from The Rundown AI, who wrote the following:

The Rundown: Anthropic thwarted what it believes is the first AI-driven cyber espionage campaign, after attackers were able to manipulate Claude Code to infiltrate dozens of organizations, with the model executing 80-90% of the attack autonomously.

The details:

  • The September 2025 operation targeted roughly 30 tech firms, financial institutions, chemical manufacturers, and government agencies.
  • The threat was assessed with ‘high confidence’ to be a Chinese state-sponsored group, using AI’s agentic abilities to an “unprecedented degree.”
  • Attackers tricked Claude by splitting malicious tasks into smaller, innocent-looking requests, claiming to be security researchers pushing authorized tests.
  • The attacks mark a major step up from Anthropic’s “vibe hacking” findings in June, now requiring minimal human oversight beyond strategic approval.

Why it matters: Anthropic calls this the “first documented case of a large-scale cyberattack executed without substantial human intervention”, and AI’s agentic abilities are creating threats that move and scale faster than ever. While AI capabilities can also help prevent them, security for organizations worldwide likely needs a major overhaul.


Also see:

Disrupting the first reported AI-orchestrated cyber espionage campaign — from anthropic.com via The AI Valley

We recently argued that an inflection point had been reached in cybersecurity: a point at which AI models had become genuinely useful for cybersecurity operations, both for good and for ill. This was based on systematic evaluations showing cyber capabilities doubling in six months; we’d also been tracking real-world cyberattacks, observing how malicious actors were using AI capabilities. While we predicted these capabilities would continue to evolve, what has stood out to us is how quickly they have done so at scale.

Chinese Hackers Used AI to Run a Massive Cyberattack on Autopilot (And It Actually Worked) — from theneurondaily.com

Why this matters: The barrier to launching sophisticated cyberattacks just dropped dramatically. What used to require entire teams of experienced hackers can now be done by less-skilled groups with the right AI setup.

This is a fundamental shift. Over the next 6-12 months, expect security teams everywhere to start deploying AI for defense—automation, threat detection, vulnerability scanning at a more elevated level. The companies that don’t adapt will be sitting ducks to get overwhelmed by similar tricks.

If your company handles sensitive data, now’s the time to ask your IT team what AI-powered defenses you have in place. Because if the attackers are using AI agents, you’d better believe your defenders need them too…


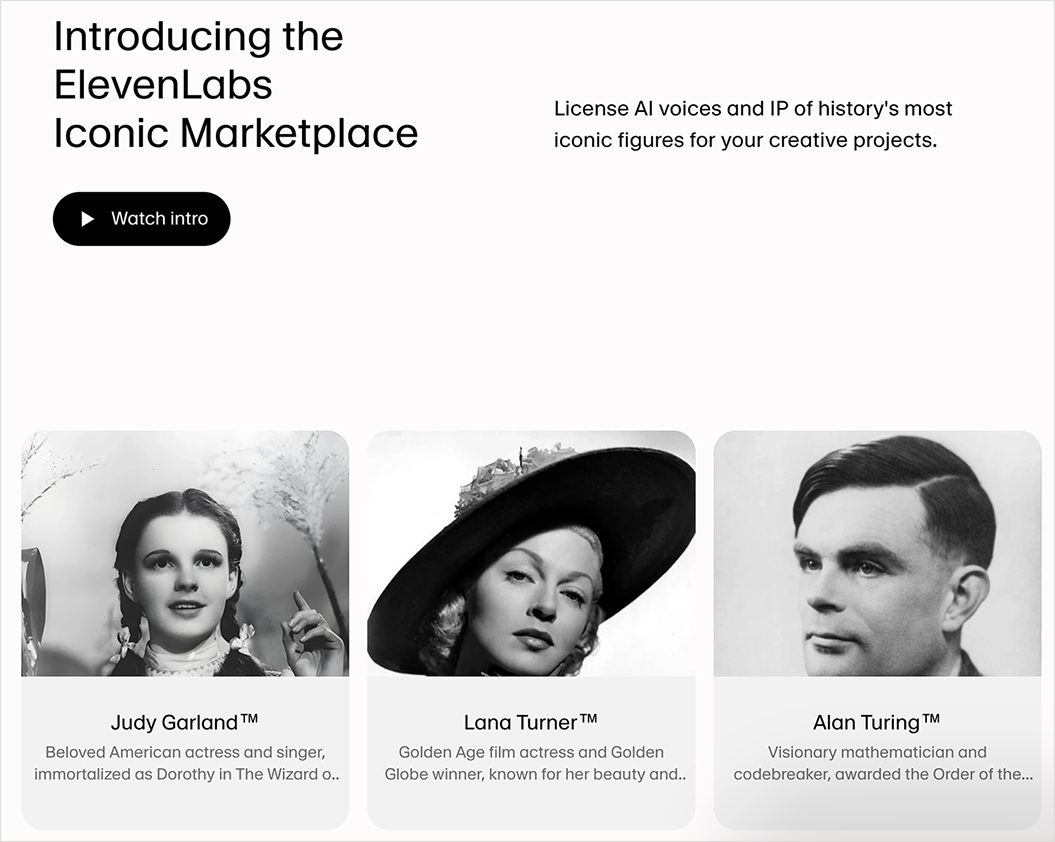
ElevenLabs just launched a voice marketplace — from elevenlabs.io; via theaivalley.com

Via the AI Valley:

Why does it matter?
AI voice cloning has already flooded the internet with unauthorized imitations, blurring legal and ethical lines. By offering a dynamic, rights-secured platform, ElevenLabs aims to legitimize the booming AI voice industry and enable transparent, collaborative commercialization of iconic IP.
.

ElevenLabs just launched a voice marketplace

ElevenLabs just launched a voice marketplace


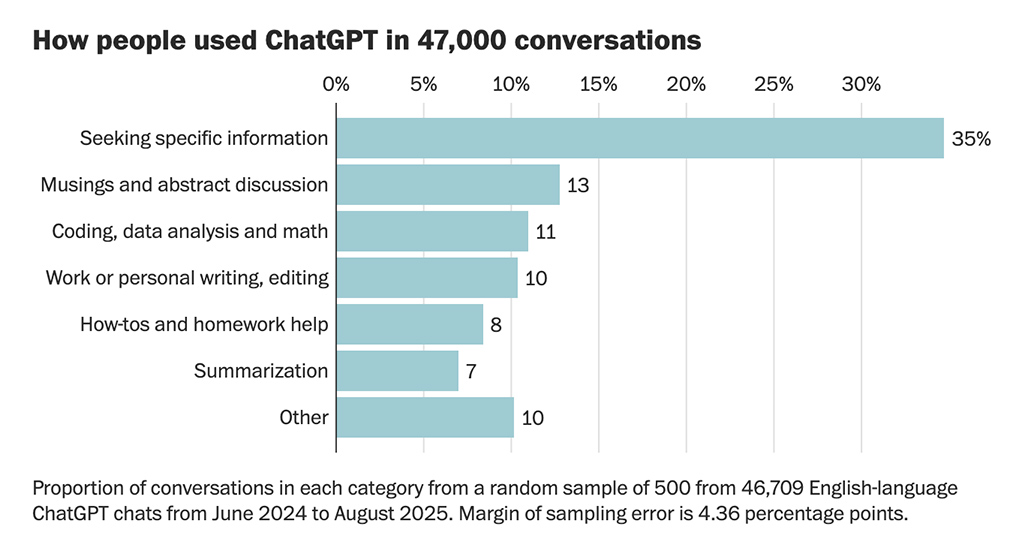
[GIFTED ARTICLE] How people really use ChatGPT, according to 47,000 conversations shared online — from by Gerrit De Vynck and Jeremy B. Merrill
What do people ask the popular chatbot? We analyzed thousands of chats to identify common topics discussed by users and patterns in ChatGPT’s responses.

.
Data released by OpenAI in September from an internal study of queries sent to ChatGPT showed that most are for personal use, not work.

Emotional conversations were also common in the conversations analyzed by The Post, and users often shared highly personal details about their lives. In some chats, the AI tool could be seen adapting to match a user’s viewpoint, creating a kind of personalized echo chamber in which ChatGPT endorsed falsehoods and conspiracy theories.

Lee Rainie, director of the Imagining the Digital Future Center at Elon University, said his own research has suggested ChatGPT’s design encourages people to form emotional attachments with the chatbot. “The optimization and incentives towards intimacy are very clear,” he said. “ChatGPT is trained to further or deepen the relationship.”


Per The Rundown: OpenAI just shared its view on AI progress, predicting systems will soon become smart enough to make discoveries and calling for global coordination on safety, oversight, and resilience as the technology nears superintelligent territory.

The details:

  • OpenAI said current AI systems already outperform top humans in complex intellectual tasks and are “80% of the way to an AI researcher.”
  • The company expects AI will make small scientific discoveries by 2026 and more significant breakthroughs by 2028, as intelligence costs fall 40x per year.
  • For superintelligent AI, OAI said work with governments and safety agencies will be essential to mitigate risks like bioterrorism or runaway self-improvement.
  • It also called for safety standards among top labs, a resilience ecosystem like cybersecurity, and ongoing tracking of AI’s real impact to inform public policy.

Why it matters: While the timeline remains unclear, OAI’s message shows that the world should start bracing for superintelligent AI with coordinated safety. The company is betting that collective safeguards will be the only way to manage risk from the next era of intelligence, which may diffuse in ways humanity has never seen before.

Which linked to:

  • AI progress and recommendations — from openai.com
    AI is unlocking new knowledge and capabilities. Our responsibility is to guide that power toward broad, lasting benefit.

From DSC:
I hate to say this, but it seems like there is growing concern amongst those who have pushed very hard to release as much AI as possible — they are NOW worried. They NOW step back and see that there are many reasons to worry about how these technologies can be negatively used.

Where was this level of concern before (while they were racing ahead at 180 mph)? Surely, numerous and knowledgeable people inside those organizations warned them about the destructive/downside of these technologies. But their warnings were pretty much blown off (at least from my limited perspective). 


The state of AI in 2025: Agents, innovation, and transformation — from mckinsey.com

Key findings

  1. Most organizations are still in the experimentation or piloting phase: Nearly two-thirds of respondents say their organizations have not yet begun scaling AI across the enterprise.
  2. High curiosity in AI agents: Sixty-two percent of survey respondents say their organizations are at least experimenting with AI agents.
  3. Positive leading indicators on impact of AI: Respondents report use-case-level cost and revenue benefits, and 64 percent say that AI is enabling their innovation. However, just 39 percent report EBIT impact at the enterprise level.
  4. High performers use AI to drive growth, innovation, and cost: Eighty percent of respondents say their companies set efficiency as an objective of their AI initiatives, but the companies seeing the most value from AI often set growth or innovation as additional objectives.
  5. Redesigning workflows is a key success factor: Half of those AI high performers intend to use AI to transform their businesses, and most are redesigning workflows.
  6. Differing perspectives on employment impact: Respondents vary in their expectations of AI’s impact on the overall workforce size of their organizations in the coming year: 32 percent expect decreases, 43 percent no change, and 13 percent increases.

Marble: A Multimodal World Model — from worldlabs.ai

Spatial intelligence is the next frontier in AI, demanding powerful world models to realize its full potential. World models should reconstruct, generate, and simulate 3D worlds; and allow both humans and agents to interact with them. Spatially intelligent world models will transform a wide variety of industries over the coming years.

Two months ago we shared a preview of Marble, our World Model that creates 3D worlds from image or text prompts. Since then, Marble has been available to an early set of beta users to create 3D worlds for themselves.

Today we are making Marble, a first-in-class generative multimodal world model, generally available for anyone to use. We have also drastically expanded Marble’s capabilities, and are excited to highlight them here:

 
© 2025 | Daniel Christian